One door,
not a ring of keys.
Smartplane sits between your AI agents and your company's tools. Everyone adds one MCP URL to Claude Code, Cursor or ChatGPT. You decide what each person's agent can reach, write the rules it must follow, and keep a record of every call.
Free for up to 10 people. Works with any client that speaks MCP.
~/grace/project/.mcp.json
{
  "mcpServers": {
    "github":      { "command": "npx", "args": ["@mcp/github"], "env": { "GITHUB_TOKEN": "ghp_r8Kq2vT…" } },Grace's personal token, scopes repo and admin:org
    "linear":      { "url": "https://mcp.linear.app/sse" },
    "postgres":    { "command": "npx", "args": ["@mcp/postgres", "postgres://admin:pw@prod-db:5432/app"] },Production database, read and write
    "stripe":      { "command": "npx", "args": ["@stripe/mcp"], "env": { "STRIPE_KEY": "sk_live_51Hx…" } },Live key. It can issue refunds of any size
    "slack":       { "command": "npx", "args": ["@mcp/slack"], "env": { "SLACK_BOT_TOKEN": "xoxb-2291…" } },
    "gdrive":      { "command": "npx", "args": ["@mcp/gdrive"], "env": { "CREDS": "~/Downloads/creds (2).json" } },
    "notion":      { "url": "https://mcp.notion.com/mcp" },
    "sentry":      { "command": "npx", "args": ["@sentry/mcp"], "env": { "SENTRY_TOKEN": "sntrys_eyJ…" } },
    "datadog":     { "command": "npx", "args": ["dd-mcp"], "env": { "DD_API_KEY": "4f1c9e…" } },
    "jira":        { "command": "uvx", "args": ["mcp-atlassian"], "env": { "JIRA_TOKEN": "ATATT3x…" } },
    "snowflake":   { "command": "uvx", "args": ["snowflake-mcp"], "env": { "SF_PASSWORD": "Winter2025!" } },A shared password, in plain text, on a laptop
    "aws":         { "command": "uvx", "args": ["aws-mcp"], "env": { "AWS_SECRET_ACCESS_KEY": "wJalr…" } },
    "billing-api": { "url": "https://billing.internal/mcp", "headers": { "Authorization": "Bearer eds_7Qm…" } },Edsger's token. He left in September
    "figma":       { "url": "http://127.0.0.1:3845/mcp" }
    "smartplane":  { "url": "https://app.smartplane.dev/mcp" }
  }
}
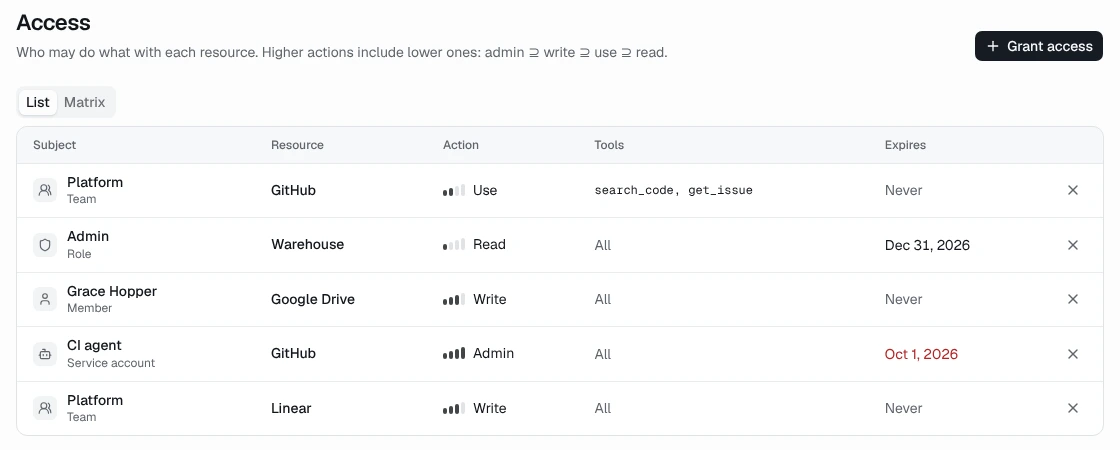
Grace signs in once with her work account. Her agent now sees GitHub, Linear and Google Drive, because her team does. Nobody's laptop holds a key, and this is the admin view of who can reach what:
Every agent got its own keys.
When a team adopts agents, each engineer wires up their own: an MCP server per tool, a personal token per server, a database URL copied from the wiki. It works on Monday. By the end of the quarter nobody can say who can reach payroll, the support bot holds a live Stripe key, and the person who left in September is still connected through a token in someone's dotfile.
Security can't see it. Platform can't fix it without breaking everyone's setup. And nothing stops an agent from running DELETE on the wrong table, because nobody ever wrote down that it shouldn't.
Decide who reaches what.
Grant tools to a person, team, role or service account. Their agents see those and nothing else.
- MCP servers and tools
- Register GitHub, Linear or your own server once. Grant the whole server or two tools from it, like
search_codeandget_issue. - Databases
- Read-only unless you say otherwise. Writes need a grant at the write level, and a rule can still hold them for approval.
- Internal APIs
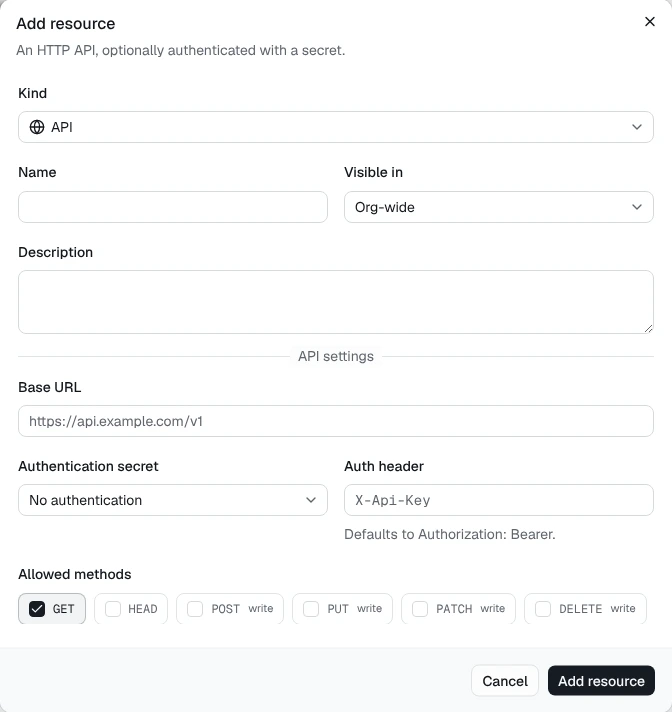
- Point at a base URL and tick the methods agents may call.
GETis on by default;POST,PUT,PATCHandDELETEcount as writes. - Secrets
- Envelope-encrypted and injected on the server when the call is made. The agent never sees the value, and neither does the person.
- Variables and skills
- Shared settings and instructions, scoped to a team or a project, so everyone's agent starts from the same place.
- Expiry
- Give the CI agent admin on GitHub until the migration ships on October 1, and it ends on October 1.
Write the rules in plain English.
Type the rule the way you'd say it in a meeting. Smartplane compiles it into a classifier and checks every agent action against it before the action runs.
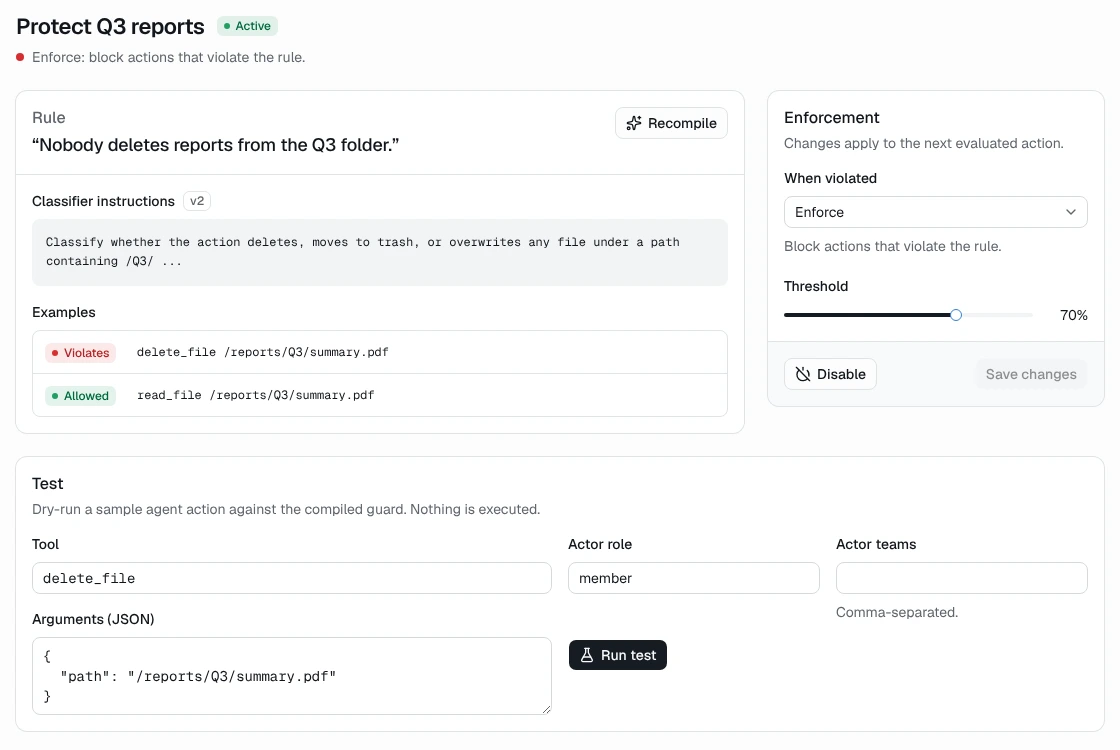
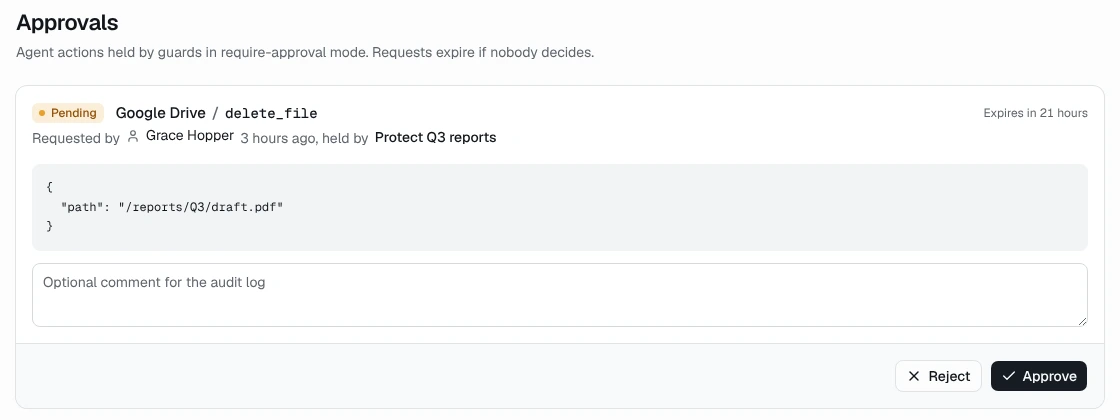
Each rule chooses what happens on a match: block the action, flag it in the log and let it through, or hold it until someone approves. Approvers are people with the right role, and nobody can approve their own request.
If the classifier can't be reached and an enforcing rule applies, the action is denied. Rules fail closed.
| The agent tries | On behalf of | Rule | Result |
|---|---|---|---|
read_file /reports/Q3/summary.pdf | Grace, Claude Code | Nobody deletes reports from the Q3 folder | Allowed |
delete_file /reports/Q3/summary.pdf | Grace, Claude Code | Nobody deletes reports from the Q3 folder | Blocked before it ran |
refunds.create amount=1200 USD | Support agent | Only the finance team can issue refunds over $500 | Held for finance |
UPDATE invoices SET status='void' | Ada, Cursor | No writes to production | Held; Ada can't approve it |
delete_file /reports/Q3/draft.pdf | CI agent | Classifier unreachable | Denied, fails closed |
Leavers lose access in one step.
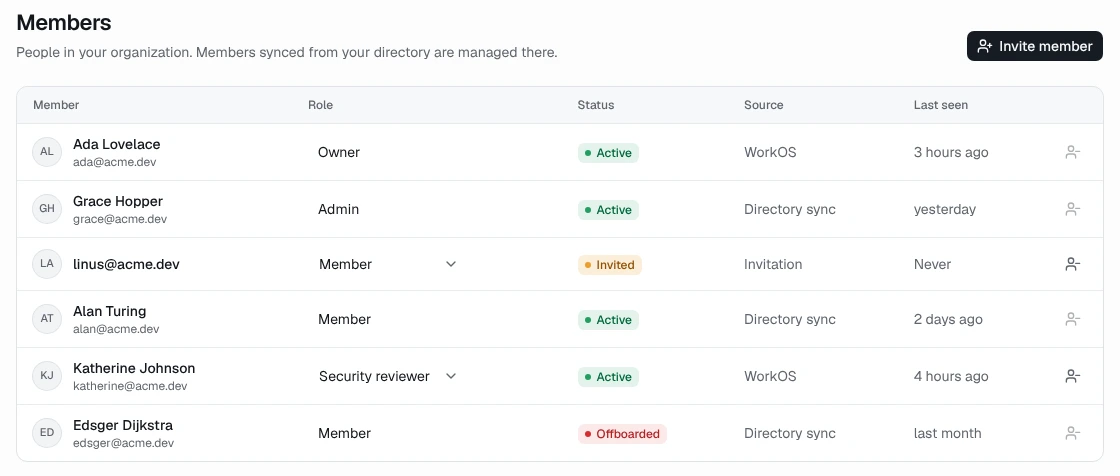
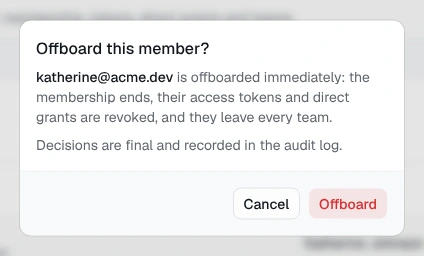
When someone is removed in your directory, Smartplane hears it over SCIM and runs one offboarding path. Their agents fail on the next call.
Edsger's membership 3 access tokens 2 direct grants the Platform team
Every call, on the record.
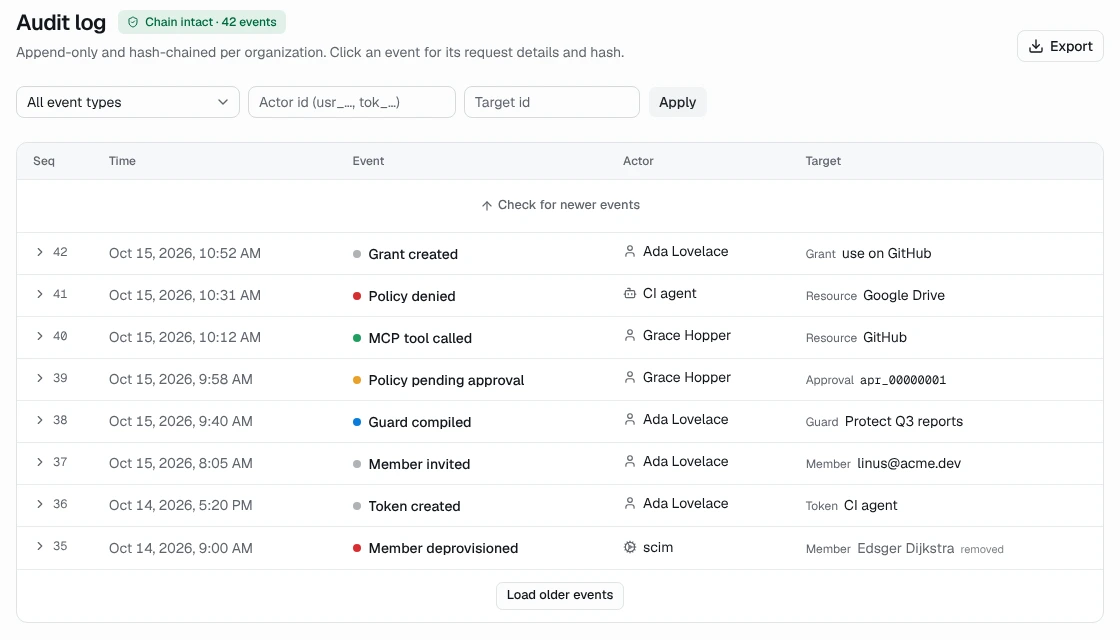
Tool calls, denials, approvals, grant changes and sign-ins go into an append-only log. Each event carries the hash of the one before it, so a deleted or edited row breaks the chain and shows.
What your SOC 2 auditor asks for, already kept
| Criterion | Evidence Smartplane produces |
|---|---|
| CC6.1 Logical access | Grants by person, team, role and project. Secrets envelope-encrypted, never returned by the API or shown to agents. |
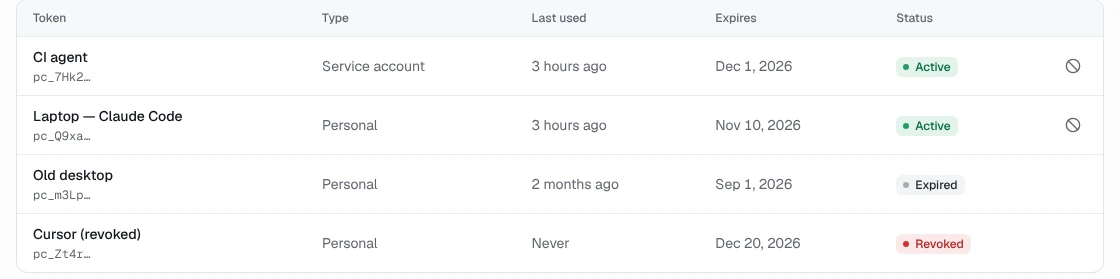
| CC6.2 Granting access | Members come from your directory through WorkOS SSO and SCIM. Access tokens are stored as hashes and expire within 90 days. |
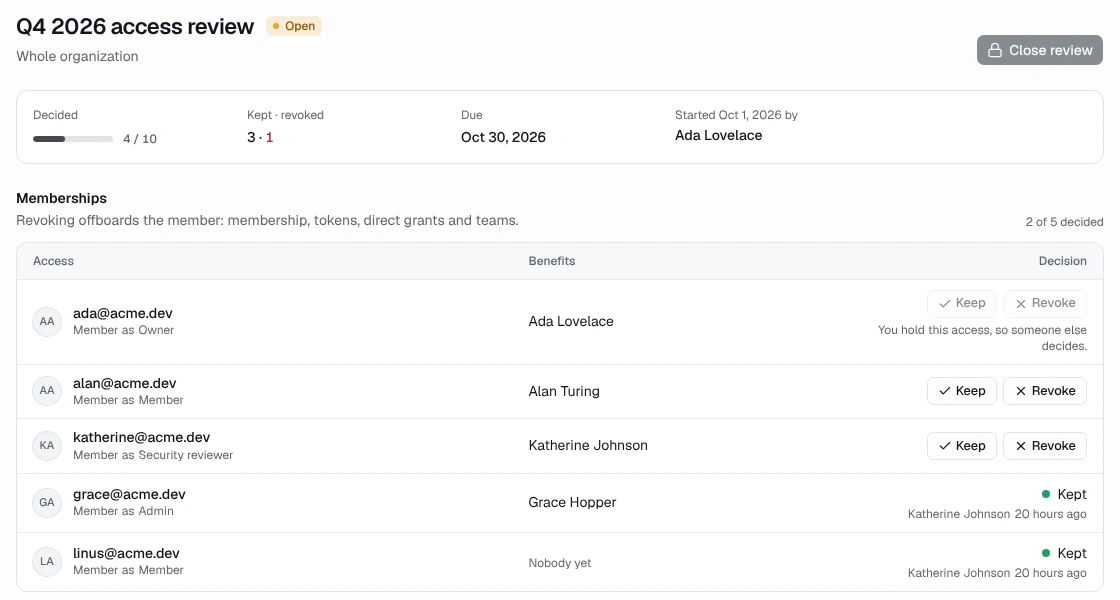
| CC6.3 Removing access | One offboarding path for leavers, plus quarterly access reviews where every keep or revoke is recorded with who decided. |
| CC7.2 Monitoring | A hash-chained event log per organisation with a one-click integrity check and CSV or JSON export for the audit window. |
Works with the agents you use.
Claude Code, Cursor, ChatGPT, VS Code and your own agents all speak MCP. Clients that support MCP sign-in only need the URL; they open a browser, you log in with your work account, and access ends when your membership does. For CI and older clients, mint a token: it's shown once, stored as a hash, and expires.
claude mcp add --transport http smartplane https://app.smartplane.dev/mcpRuns on Cloudflare's network, close to wherever your agents run.
Start with your own team.
| Plan | FreeTeamup to 10 people | $15Businessper person, per month | Let's talkEnterpriseannual agreement |
|---|---|---|---|
| One MCP URL, OAuth sign-in | Yes | Yes | Yes |
| Resources and grants | 5 resources | Unlimited | Unlimited |
| Plain-English rules | Flag only | Block, flag, hold | Block, flag, hold |
| Approvals | Yes | Yes | |
| Audit log history | 30 days | 1 year | 7 years, with export |
| Access reviews | Yes | Yes | |
| SSO and SCIM | Yes, via WorkOS | ||
| Security review, DPA, SLA | Yes | ||
| Start free | Start a 30-day trial | Email us |
Hand out one URL.
Keep the keys.
Set up your first resource and rule in about ten minutes. Your team adds one line to their agent.
Start free